 GRC Owl
A private instance
Your own sub-domain, database, file storage and sessions, with a database login that reaches only your data.
GRC Owl brings your audits, controls and evidence, risk registers, issues, policies, action items and third-party risk into one workspace. It routes each review to the right person, flags what is overdue and records every step.
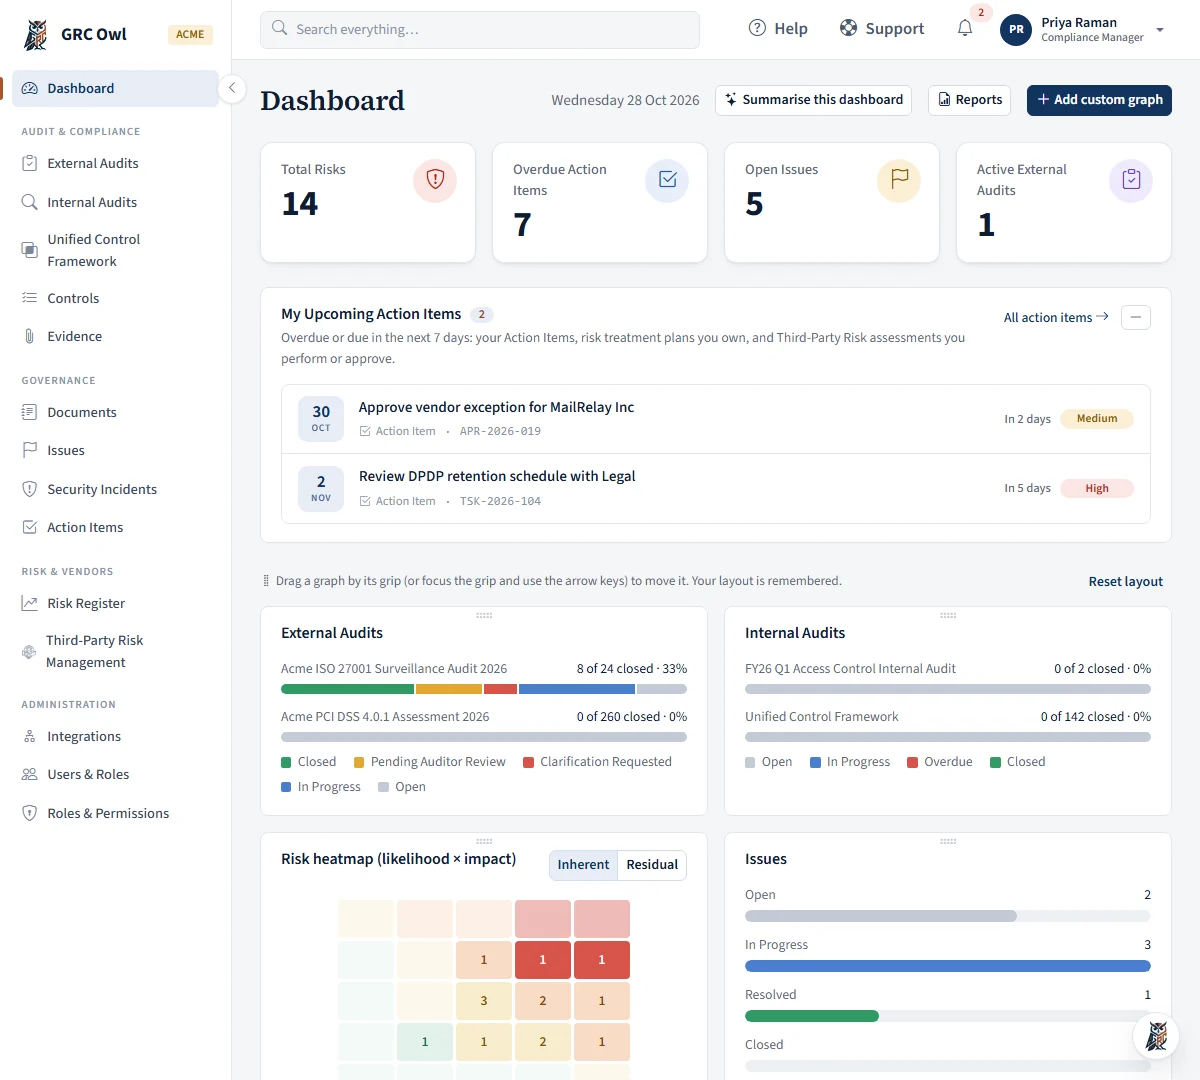
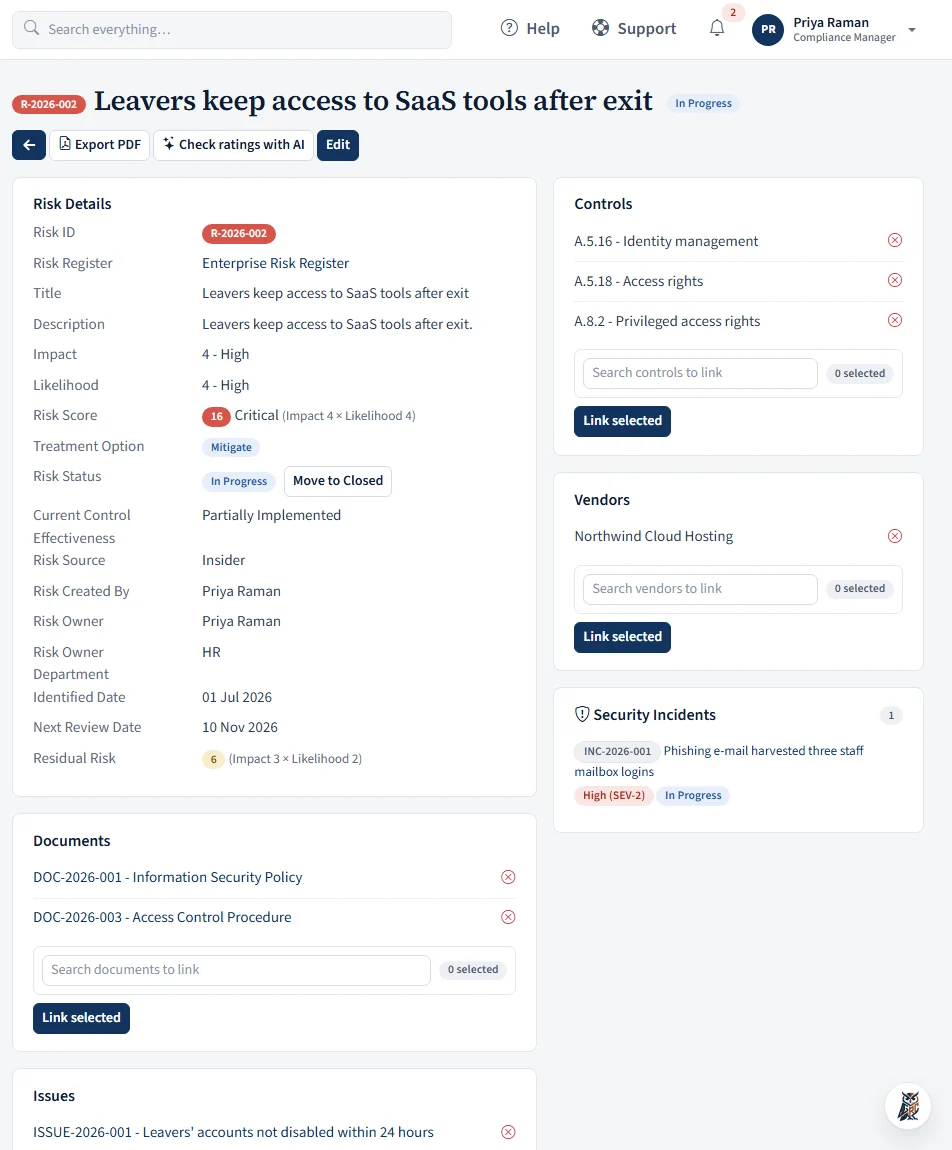
Controls link to audits, evidence links to controls, risks link to policies and vendors, and findings become issues with corrective actions. Nothing is copied between spreadsheets.
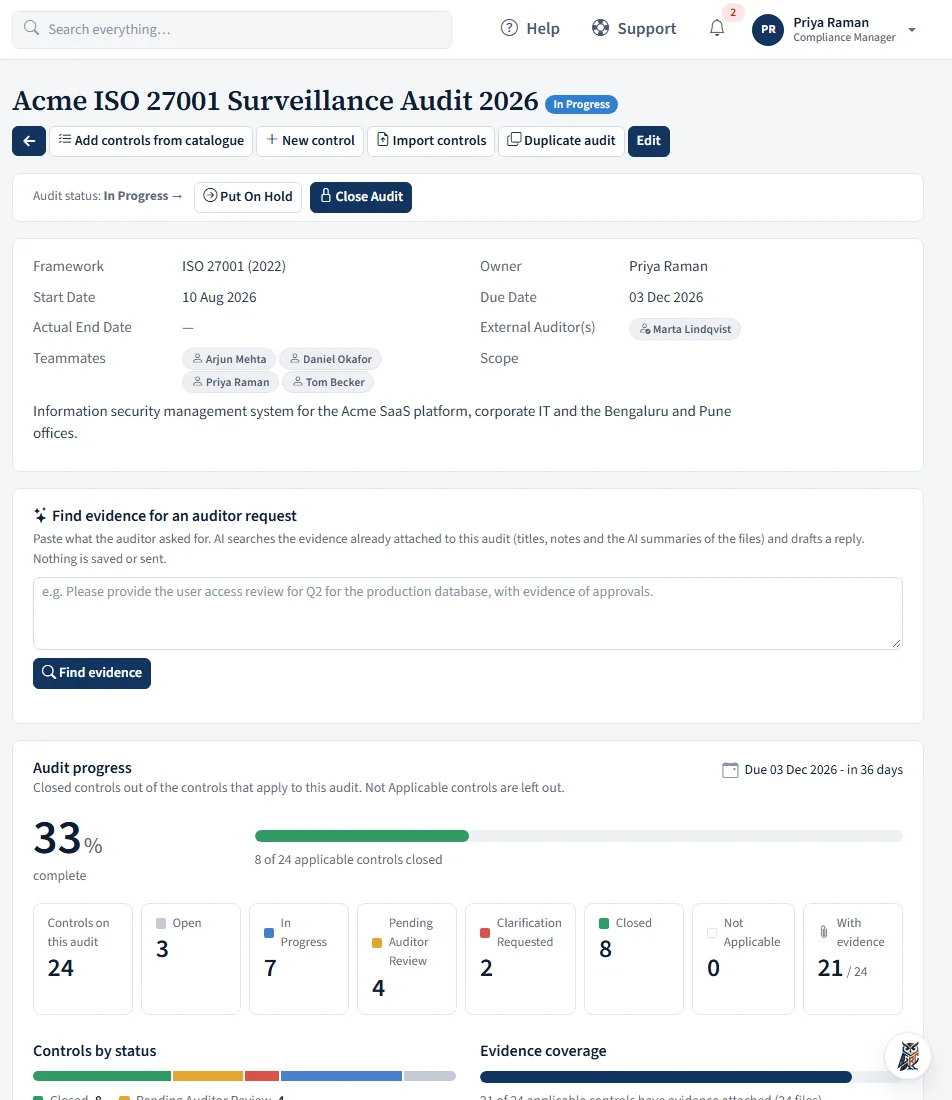
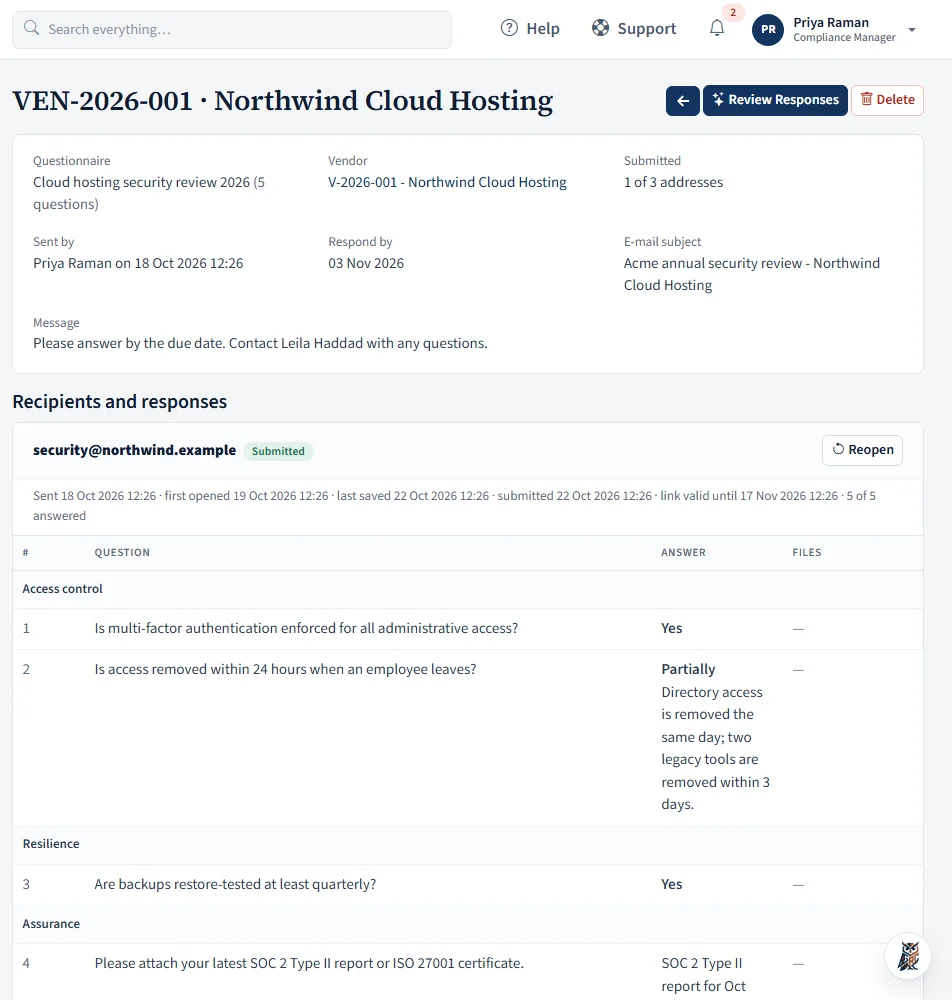
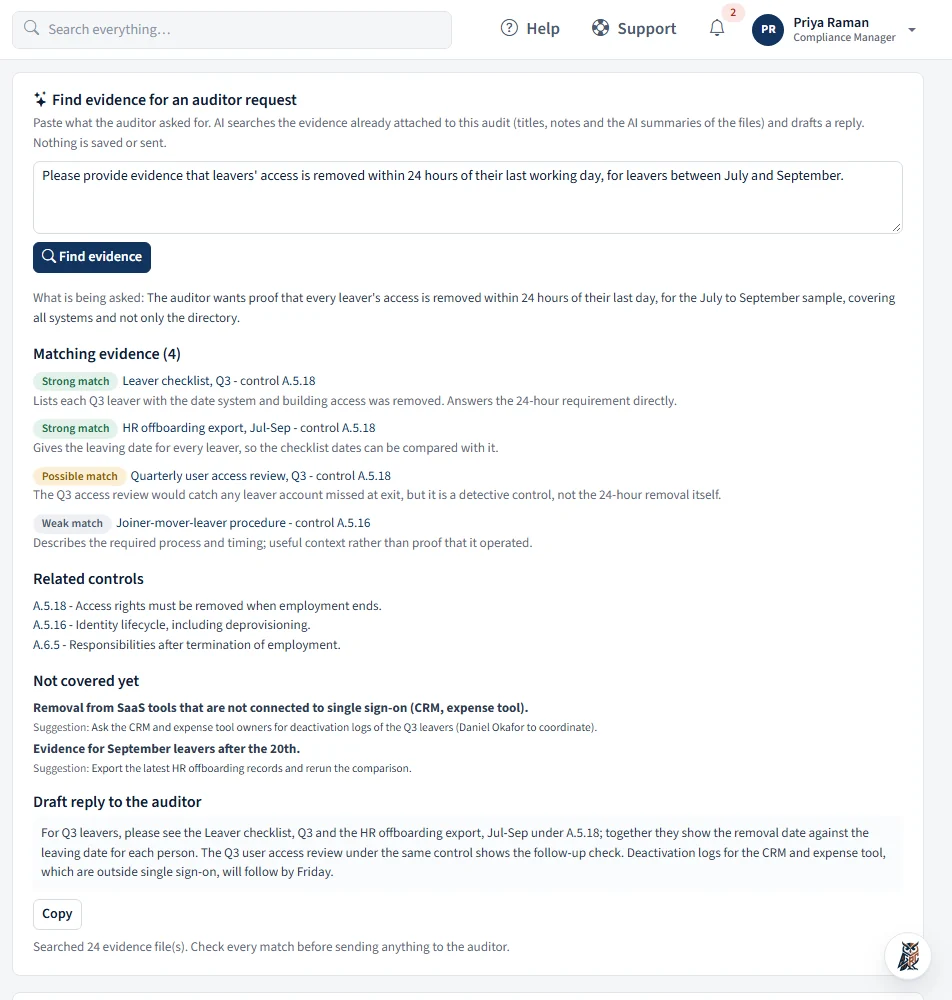
Name, framework, scope, owner, due date and your external auditors.
Built-in sets such as PCI DSS, DPDP, HIPAA and ISO 42001 load automatically. Otherwise pick from the ISO 27001 catalogue or import from Excel or CSV.
Owners and teammates upload files, comment, @mention colleagues and submit each control.
The auditor approves each control or requests clarification. Both sides get an e-mail.
Non-conformities become issues, with root cause and corrective actions tracked to closure.
Four roles out of the box, then access narrows to the record: each audit, risk register and issue has its own list of who may see it.
Users and roles, workflow design, and the System Log with per-person activity.
Audits, controls, risks, vendors, documents, issues and action items.
Their own action items and documents, and any audit they are added to as a teammate.
Approves controls or requests clarification on their own audits, and sees nothing else.
A GRC system holds where a company is exposed. GRC Owl is built around isolation, strong sign-in, least-privilege access and an audit trail that is never purged.
Your own sub-domain, database, file storage and sessions, with a database login that reaches only your data.
Microsoft Entra ID, Google Workspace, Okta or any OpenID Connect provider, limited to your domains.
Authenticator-app sign-in, and single-use reset links that never reveal whether an account exists.
Access narrows to each audit, register and issue; external auditors reach only their own audits.
Keep uploads and backups on our server, or in your own OneDrive, SharePoint, Google Drive, S3 or SFTP.
Changes, approvals, uploads and downloads logged with who and when, and never purged.
Tell us about your team and what you are audited against. We will walk you through the modules that matter to you.
Prefer e-mail? Write to sales@grcowl.com
We have received your request and will be in touch shortly.