Frameworks

Seventeen frameworks. Control sets ready to go.

Every audit and every control carries a framework. Fifteen of them ship with a complete control set, test procedures included: create an audit on one of them and the checklist arrives already filled in, and ISO 27001 controls are picked from a catalogue of clauses and Annex A. For the rest, bring your control set from Excel or CSV in minutes.

Built in

Ready-made control sets

116 requirements · catalogue

ISO/IEC 27001:2022

Management-system clauses 4 to 10 and all 93 Annex A controls, each with the text of its control statement, so an audit reads like your Statement of Applicability.

37Organizational (A.5)
8People (A.6)
14Physical (A.7)
34Technological (A.8)
  • Pick the controls in scope from the catalogue, filtered by group
  • Map risks and issues to Annex A controls
260 requirements · auto-loaded

PCI DSS 4.0.1

Every sub-requirement across all twelve requirements, each with its testing procedures.

  • A new PCI DSS audit starts with all 260 on the checklist
  • Quarterly and annual reviews on schedules
  • Service-provider assessments in Third-Party Risk
56 controls · auto-loaded

DPDP Act 2023

India's Digital Personal Data Protection Act and the final DPDP Rules 2025 as 56 testable obligations, each referenced to its section or rule.

  • Consent, notice, Data Principal rights, breaches and more
  • Test procedures for every obligation
  • Processor due diligence through Third-Party Risk
95 controls · auto-loaded

HIPAA

The Security Rule's administrative, physical and technical safeguards, plus the Privacy Rule, the Breach Notification Rule and the definitions and enforcement provisions that apply to them.

  • Each control referenced to its section of 45 CFR Part 164
  • Test procedures for every control
65 controls · auto-loaded

ISO/IEC 42001:2023

The AI management system standard: clauses 4 to 10 and the 38 Annex A controls, in plain-language wording with a test procedure for each.

  • Policies, roles, impact assessment, data and third-party use of AI
  • Grouped by clause and Annex A theme
103 controls · auto-loaded

ISO/IEC 27701:2025

The privacy information management standard: 25 clauses plus Annex A for controllers (31), processors (18) and both (29).

  • Sits beside ISO 27001 in the same workspace
  • Test procedures for every control
48 controls · auto-loaded

GDPR

Regulation (EU) 2016/679 as 48 testable obligations from Articles 5 to 49, in plain language, grouped by chapter.

  • Principles, lawful basis, data subject rights, processors, security, breaches and transfers
106 subcategories · auto-loaded

NIST CSF 2.0

All 106 subcategories across the six functions: Govern, Identify, Protect, Detect, Respond and Recover.

  • Outcome wording from the framework, with a test procedure for each
195 controls · auto-loaded

India's regulators

Seven sets for regulated entities, each broken into testable controls with a test procedure: SEBI CSCRF 2024 (31), RBI IT Governance 2023 (32), RBI Cyber Security Framework 2016 (37), RBI IT Outsourcing 2023 (29), RBI Digital Lending 2025 (20), IRDAI Cyber Security 2023 (37) and CERT-In Directions 2022 (9).

  • Pick the one that applies to your licence, or run several audits side by side
  • Link one control to several frameworks so a single piece of evidence counts everywhere
How it works

Start the audit, get the checklist

Choose PCI DSS, DPDP, HIPAA, ISO 42001, ISO 27701, GDPR, NIST CSF 2.0 or an Indian regulator's set when you create an external audit and every control arrives on it, marked Open and ready to assign. Delete the audit and its controls go with it.
Bring your own

Your control set, in minutes

These are ready to tag audits and controls. Import your control set from Excel or CSV with a full preview, and it works exactly like the built-in ones.

SOC 2Trust Services Criteria, Type I or II
SOC 1Controls over financial reporting
CustomInternal policies, contracts, sector rules
In the app

Start the audit, get the checklist

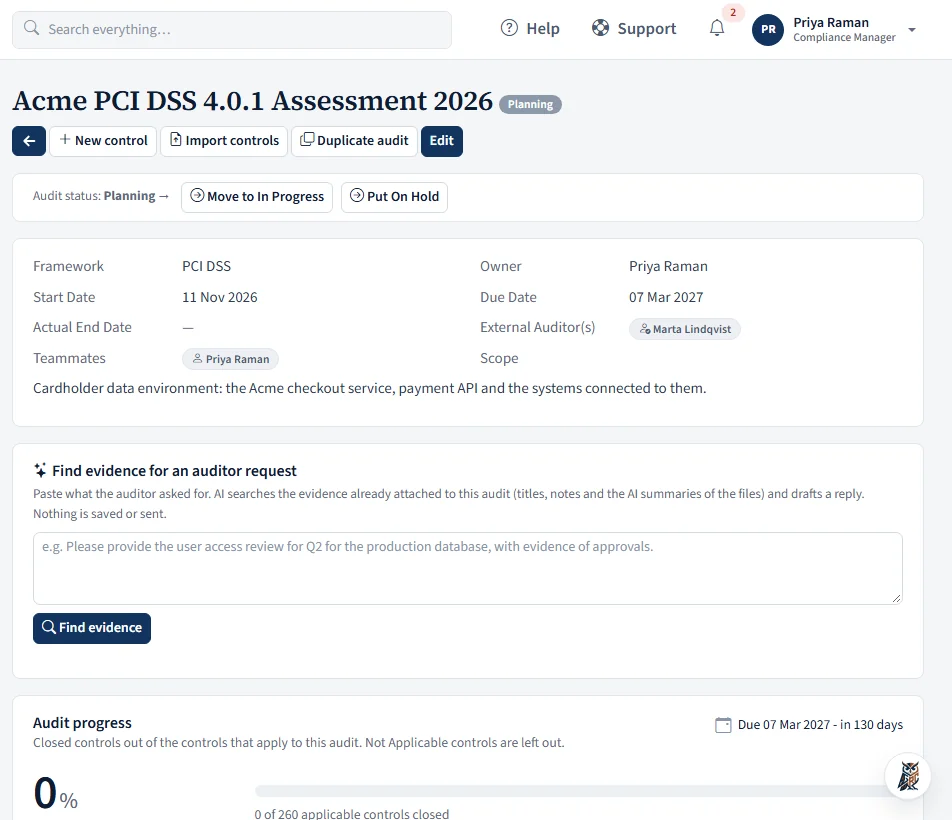
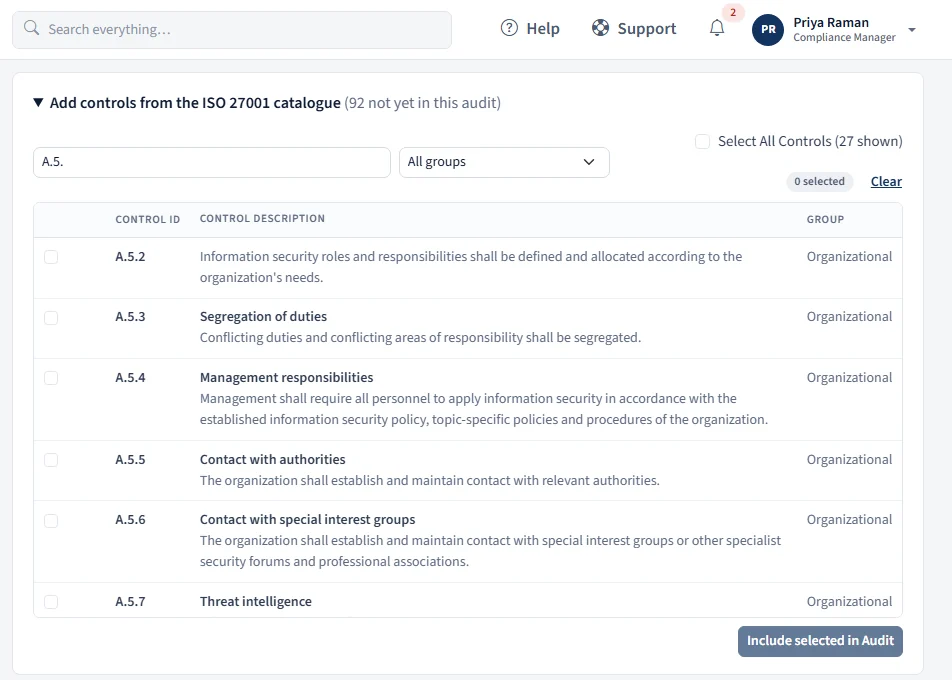
This is a PCI DSS audit moments after it was created, and the ISO 27001 catalogue you pick from. Click either picture to see it full size.

A PCI DSS 4.0.1 external audit created with all 260 requirements already on its checklist

Built-in control sets load automatically

Every requirement arrives on the audit as Open, with its test procedure, ready to assign.

The Add controls from the ISO 27001 catalogue panel with search, group filter and Select All

ISO 27001: pick the controls in scope

Search the Annex A catalogue, filter by group, tick what applies and add them in one step.

Unified Control Framework

One control library that speaks every framework

GRC Owl ships 142 common controls in 17 domains (access management, logging, vendor risk, incident response and more), each mapped to the requirements of 16 frameworks. Open one and see every requirement it satisfies.

  • Mappings are live only while an external audit uses that framework, so you never wade through requirements you are not audited on
  • For requirements nobody has mapped yet, keyword suggestions are offered for a person to confirm or remove
  • Evidence already collected for one framework can be re-used on the same control in another audit, where the audit team is allowed to see it
  • Wording is editable, and the common controls are mirrored as an internal audit you can run like any other
  • AIWith the optional AI assistant on, Rebuild Mappings reviews each live requirement and proposes the fitting common controls, with a record of every change it made
  • Not shown to external auditors
Test once, comply many

Link related controls across frameworks

A quarterly access review can serve ISO 27001, SOC 2 and PCI DSS at once. Link the related controls and the work is visible wherever it counts.

  • Linked controls shown on both sides
  • An import links a Control ID that already exists instead of duplicating it
A.5.18 Access rights · linked controls
SOC 2CC6.2 User registration and removalLinked
PCI DSS7.2.4 Review of user accountsLinked
HIPAA164.308(a)(4)(i) Information access managementLinked
Getting started

Bring your control set in an afternoon

Download the template, fill in Control ID, description, test procedures, framework and frequency, save it as Excel or CSV, and preview every row before importing. Up to 2,000 controls per file.

Talk to us about your frameworks